Important reporting obligations under the EU Cyber Resilience Act (CRA) started applying on 11 September 2026. The main provisions apply from 11 December 2027, but manufacturers of products with digital elements already have to report actively exploited vulnerabilities and severe incidents affecting product security.
An early warning may be required within 24 hours of becoming aware of the event, followed by a notification within 72 hours.
What does this mean for AGV and AMR systems?
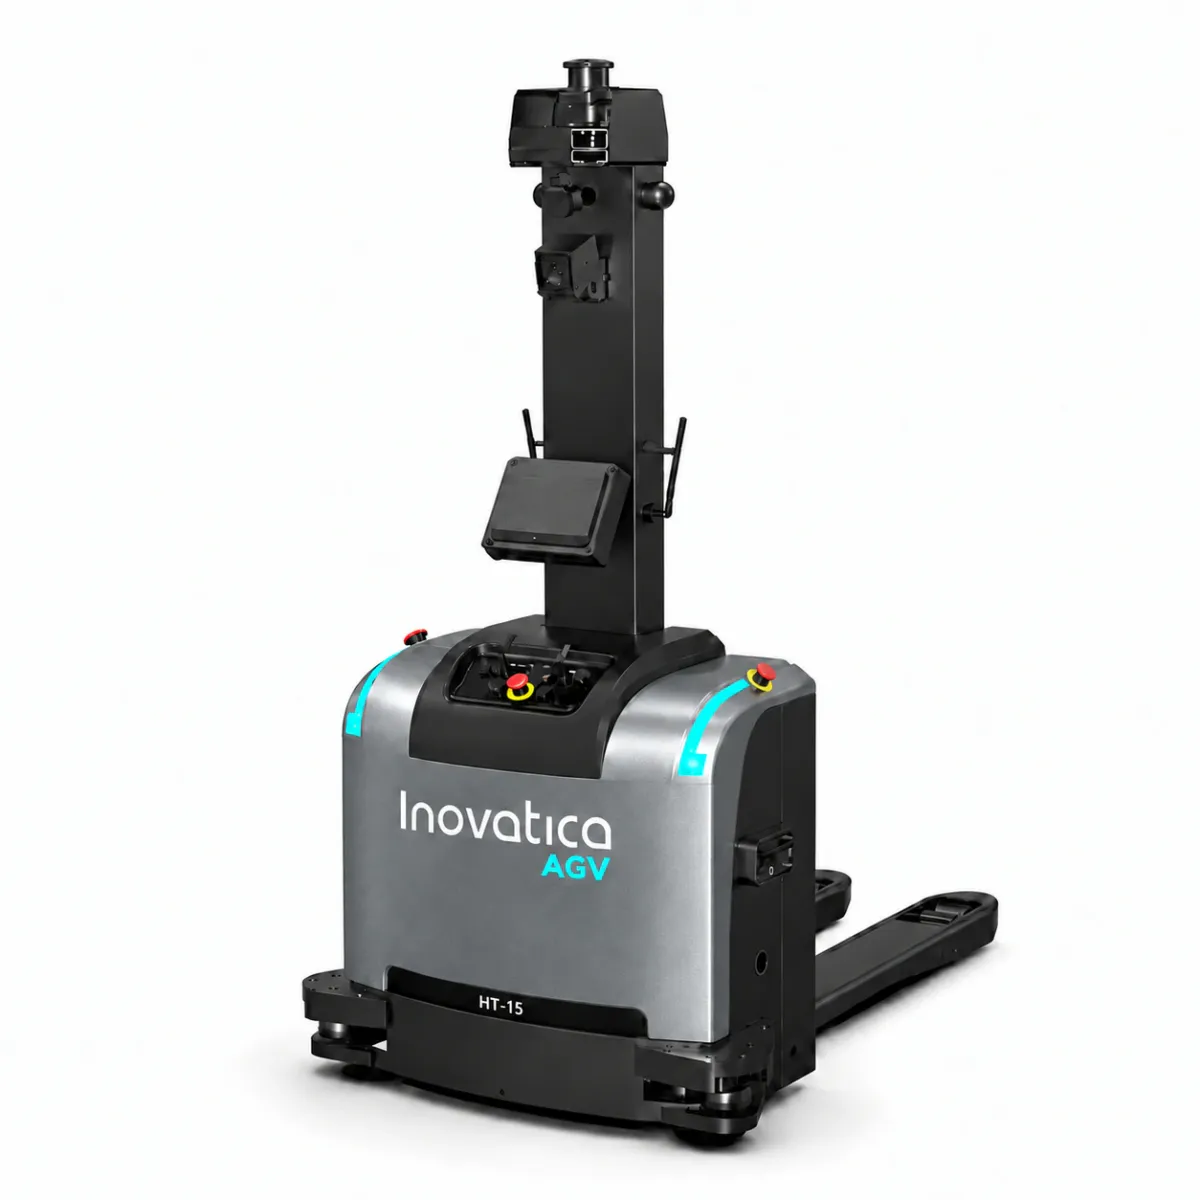
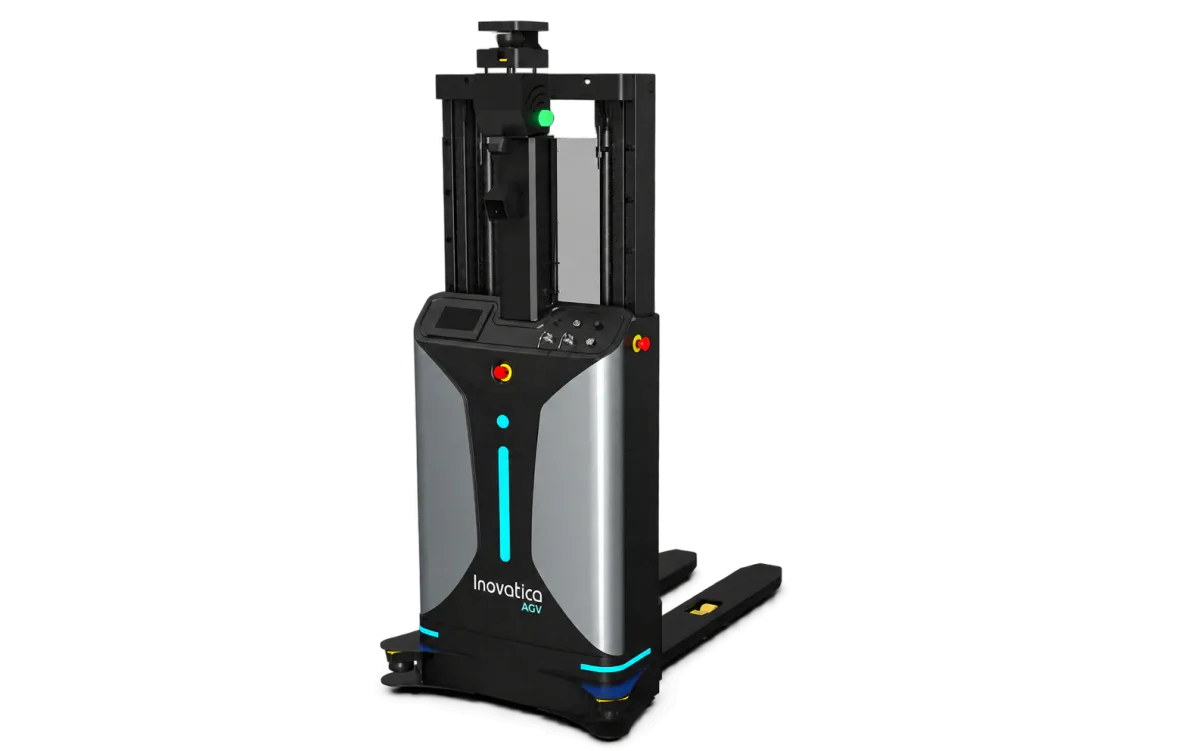
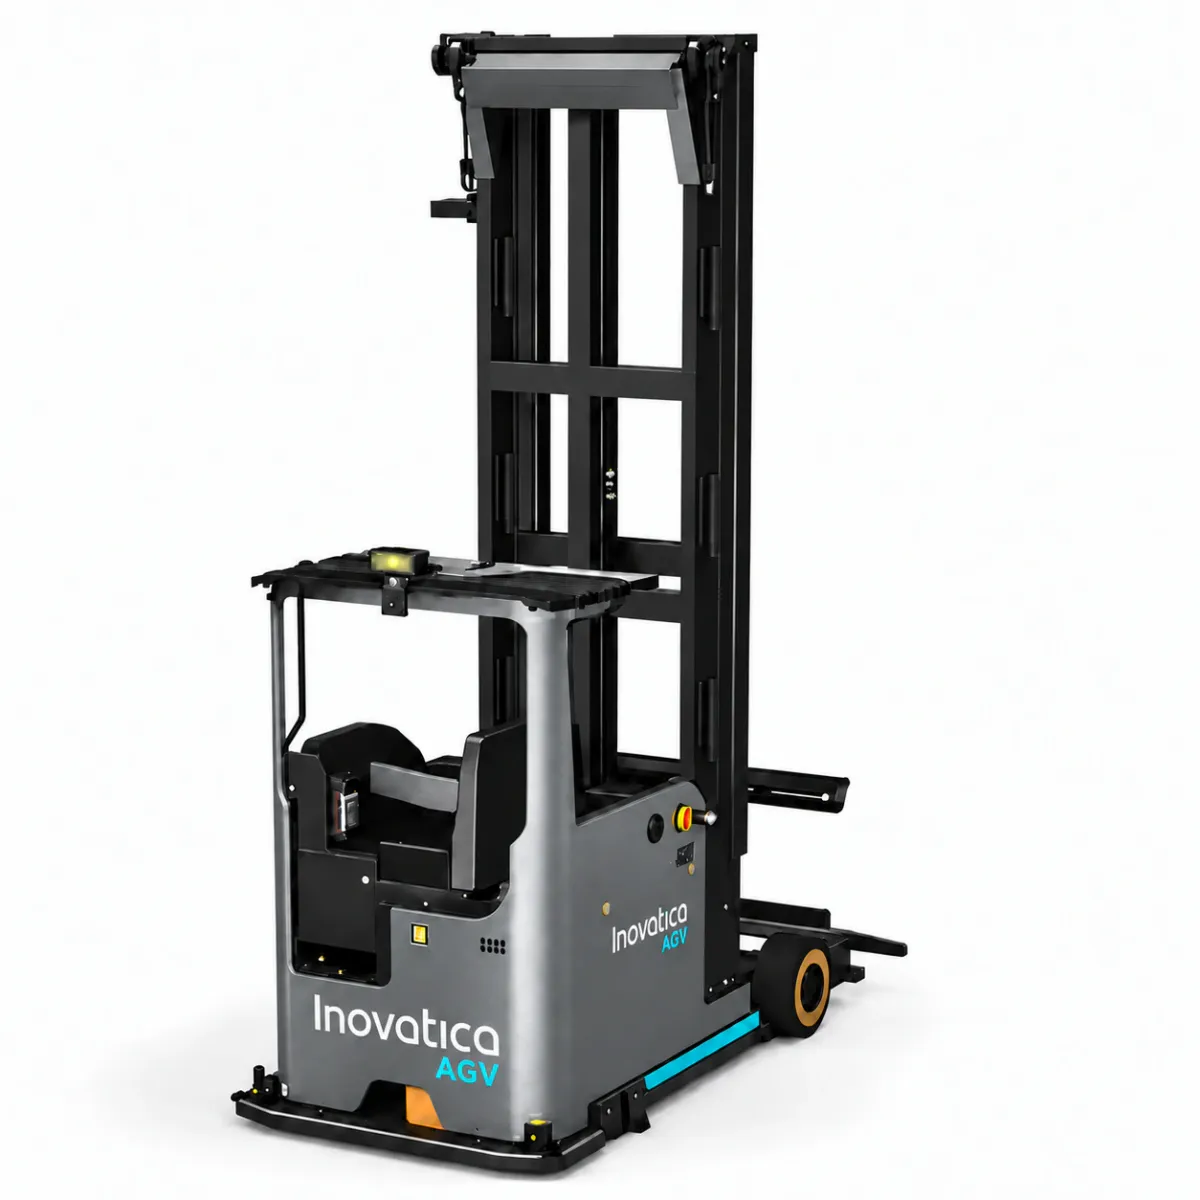
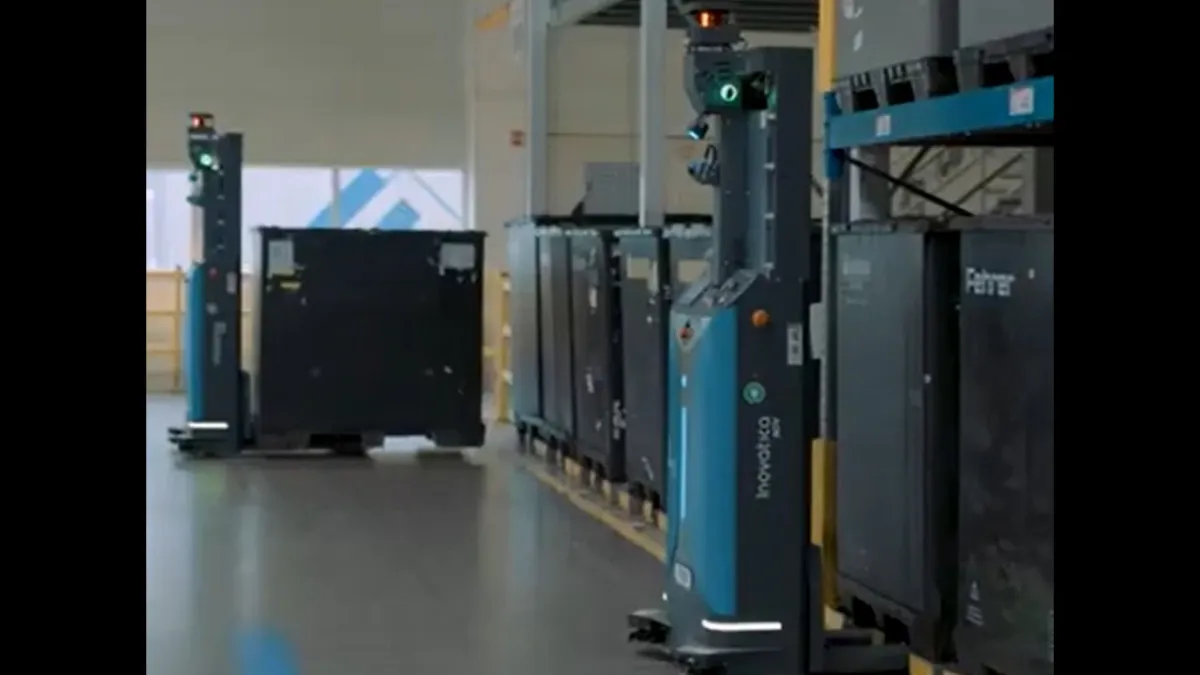
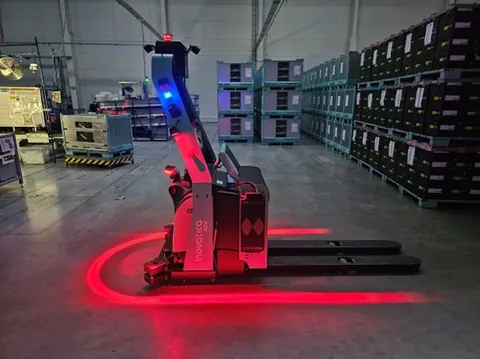
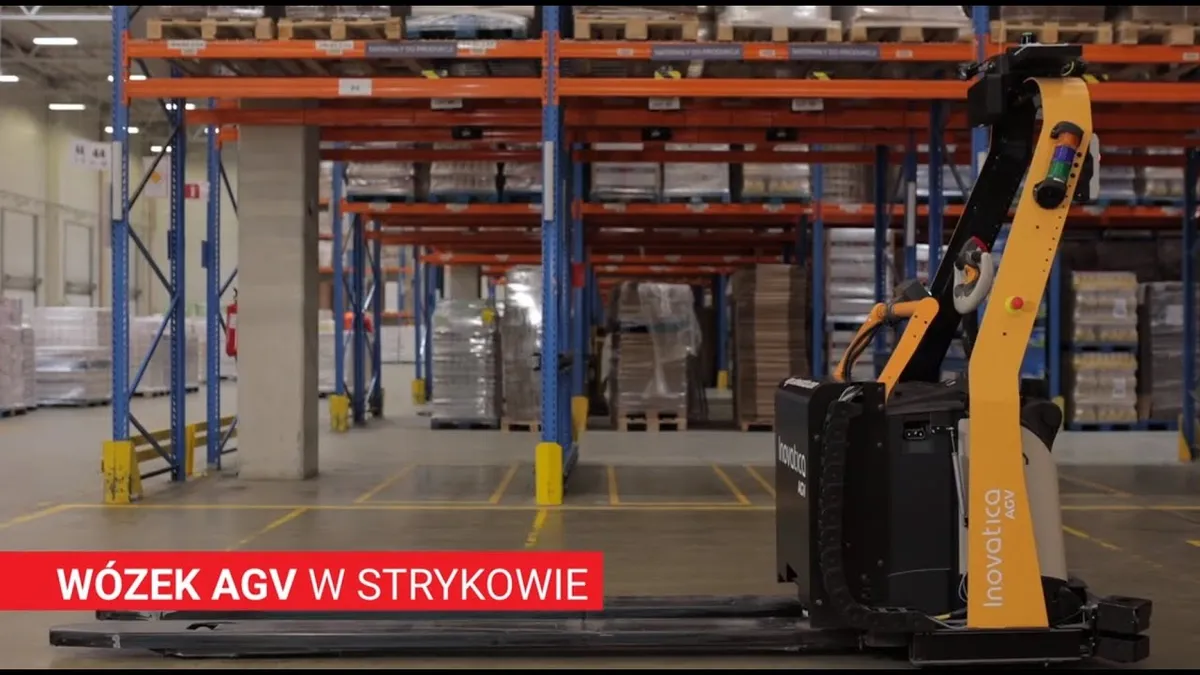
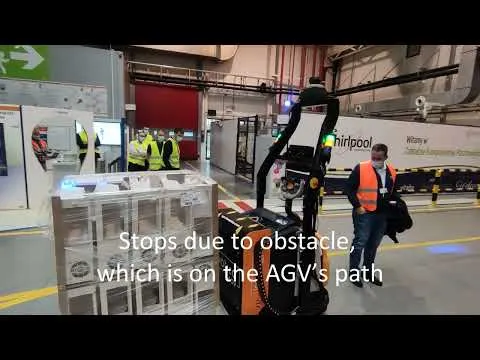
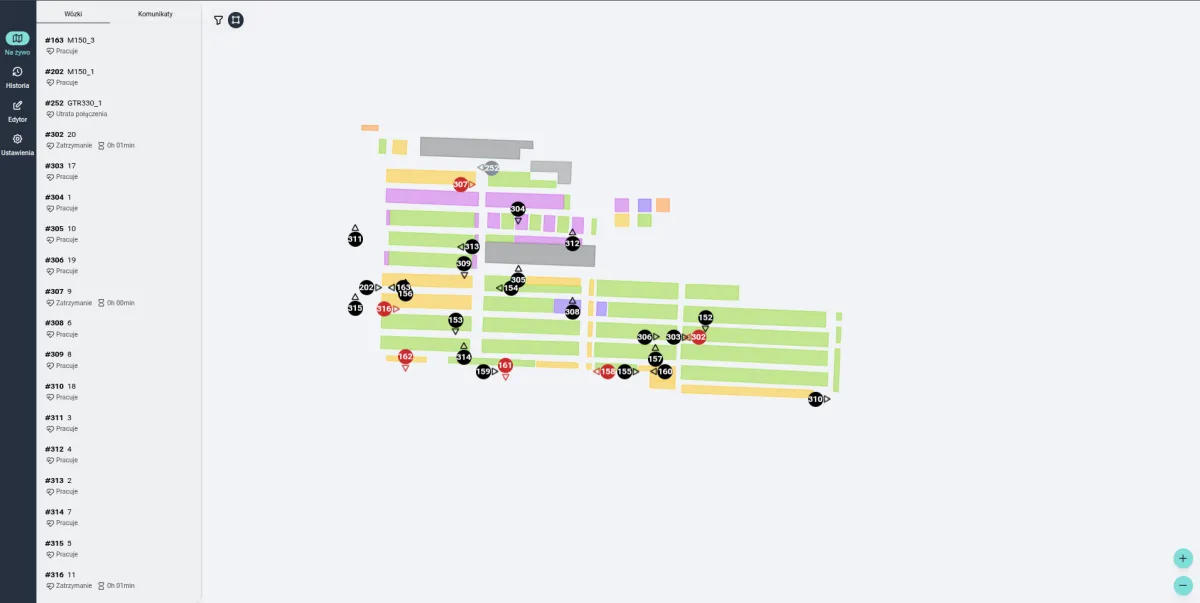
An autonomous forklift is more than a machine. It also includes an operating system, controller, Fleet Manager, software libraries, firmware, APIs and connections to the customer’s systems.
When a critical vulnerability is identified, the team needs to determine quickly:
which component → in which software version → on which robot → at which customer installation is affected.
With dozens of robots across multiple installations, establishing this manually can be difficult.
Security & Lifecycle Management for mobile robots
At Inovatica AGV, we are working on a tool concept intended to automate this information-gathering process.
The system is intended to collect installation configurations, software versions and component information, build a Software Bill of Materials (SBOM), monitor newly reported vulnerabilities and identify the specific robots and customers affected.
For example:
detected vulnerability → component → software version → 11 robots → 3 customer installations → required action.
The aim is not to update robots automatically or report incidents automatically. In an industrial environment, these decisions must remain controlled.
The primary purpose is to give the technical team reliable information for a timely decision.
Cybersecurity is becoming part of the AGV lifecycle
We see a change extending beyond CRA itself.
Managing software versions, vulnerabilities, security updates and configuration history will increasingly become a normal part of maintaining autonomous logistics systems, much like technical inspections and spare-parts management today.
For customers in automotive, manufacturing and critical infrastructure, this will also increasingly form part of supplier assessment at the request-for-quotation stage.
We therefore treat AGV cybersecurity as part of the system’s whole lifecycle: deployment, service, updates and eventual decommissioning.
Dates and reporting scope: European Commission — CRA reporting obligations and summary of the regulation. The reporting duty concerns the events specified in the regulation; discovering any vulnerability does not automatically mean the same reporting obligation applies.